
Why NAT (Network Address Translation) Still Matters in 2025
How NAT lets devices share a public address, how replies find their way back, and what address sharing changes for security, applications and operator choice.
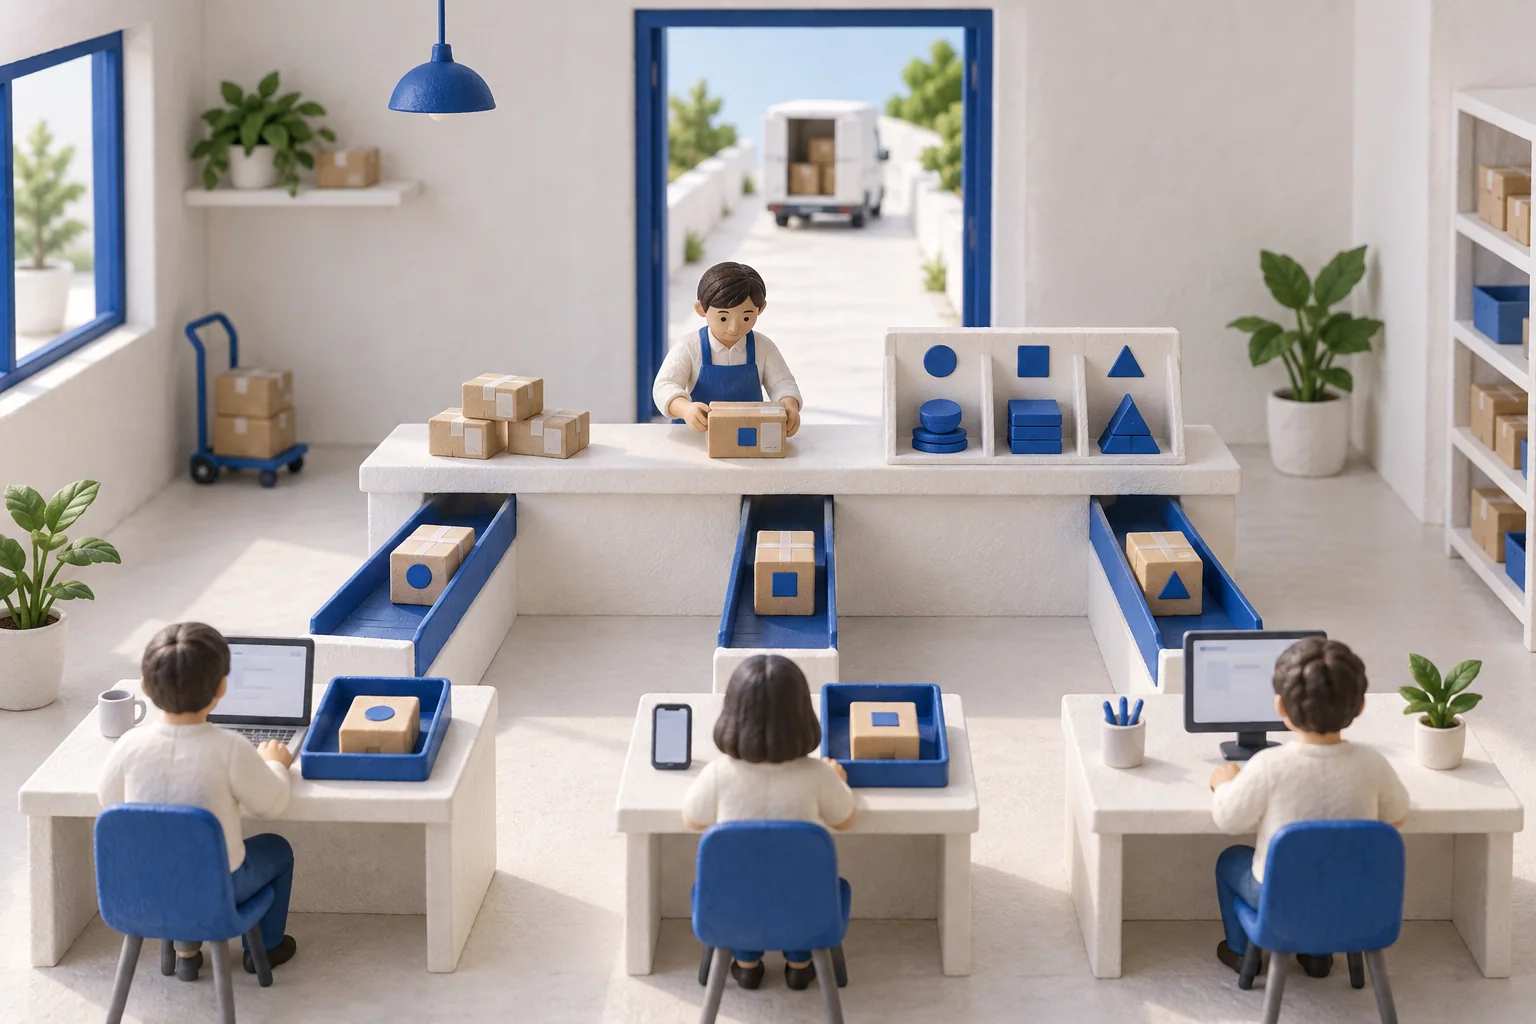
Your phone and laptop open different websites at the same time. To those sites, both connections may appear to come from one public IPv4 address. Yet each reply reaches the right screen. The home router keeps a translation record that makes this possible.
This everyday example explains why NAT still matters. It lets a network share public addresses. Understanding the extra work it creates is just as important as understanding what it saves.
One outside address, several conversations
NAT means network address translation. Basic NAT changes one address into another. The many-to-one arrangement common in home routers also translates transport ports; it is often called PAT or NAPT. A port helps distinguish one conversation from another.
Imagine a building where several desks send parcels through one reception counter. The counter needs a record of which replies belong to which desk. Similarly, the router records the mapping between an internal address and port and the address and port used outside. The traditional NAT specification describes these two forms of translation.
NAT does not create more IPv4 numbers. It allows those numbers to serve more connections, within the translator's capacity and the requirements of the applications involved.
Where does it help?
A household can connect several devices without assigning each a public address. A business can give internal systems outbound access through a shared gateway. An Internet provider can place translation in its own network, sharing public addresses among subscribers; that arrangement is called carrier-grade NAT.
The location matters. You may control your own router's mappings, while having little control over a provider's translator. That difference becomes visible when you want to accept incoming connections or diagnose a failure.
What does sharing cost?
A translator has to retain connection state and enough usable ports. It must cope with peaks, timeouts and equipment failure. Some applications need special arrangements to accept incoming traffic or work across multiple translation layers.
At provider scale, a public address alone may not identify the subscriber involved in a connection. Port information and time can also matter. The IETF's carrier-grade NAT requirements address resource limits, behaviour and logging. These are operating responsibilities, not reasons to assume NAT is always good or always bad.
Does NAT make a network secure?
Address translation and access control do different jobs. Some common NAT configurations leave unsolicited incoming traffic without a mapping, but that is not the same as a complete security policy. A router that also acts as a firewall can enforce rules about which traffic is allowed.
The distinction is explicit in the IETF's network-protection guidance: translation itself does not provide security. Nor does sharing a public address make a user anonymous. Accounts, applications and other data can still identify activity.
Is NAT the same as an IPv6 transition?
No. Ordinary IPv4 NAT translates IPv4 addresses. Dual stack means running IPv4 and IPv6; it does not automatically translate between them. Mechanisms such as NAT64 have a different job, translating between protocol versions. Keeping those terms separate helps avoid buying a solution to the wrong problem.
For a beginner, start with the actual requirement: reaching websites, accepting connections, joining networks or supporting a particular application. Then compare the operational options.
Why the choice belongs with the network operator
Lu Heng's Note 45 challenges the idea that a registry's exhausted allocation pool settles every operator's engineering choices. NAT is one useful example of why the raw address count cannot describe the whole network. Address sharing changes what a public address can serve, while bringing its own costs.
The choice should therefore rest on the service and its full operating cost: shared addresses, dedicated public addresses, IPv6 or a combination. It should not rest on a slogan about inevitable migration, or a promise that translation solves everything. Continue with what adding IPv6 changes—and what it leaves to maintain.