
Who controls the Internet? IP addresses, names and networks
Follow a website’s names, numbers and network connections to see where power sits — and why Lu Heng argues that critical administrators must be replaceable.
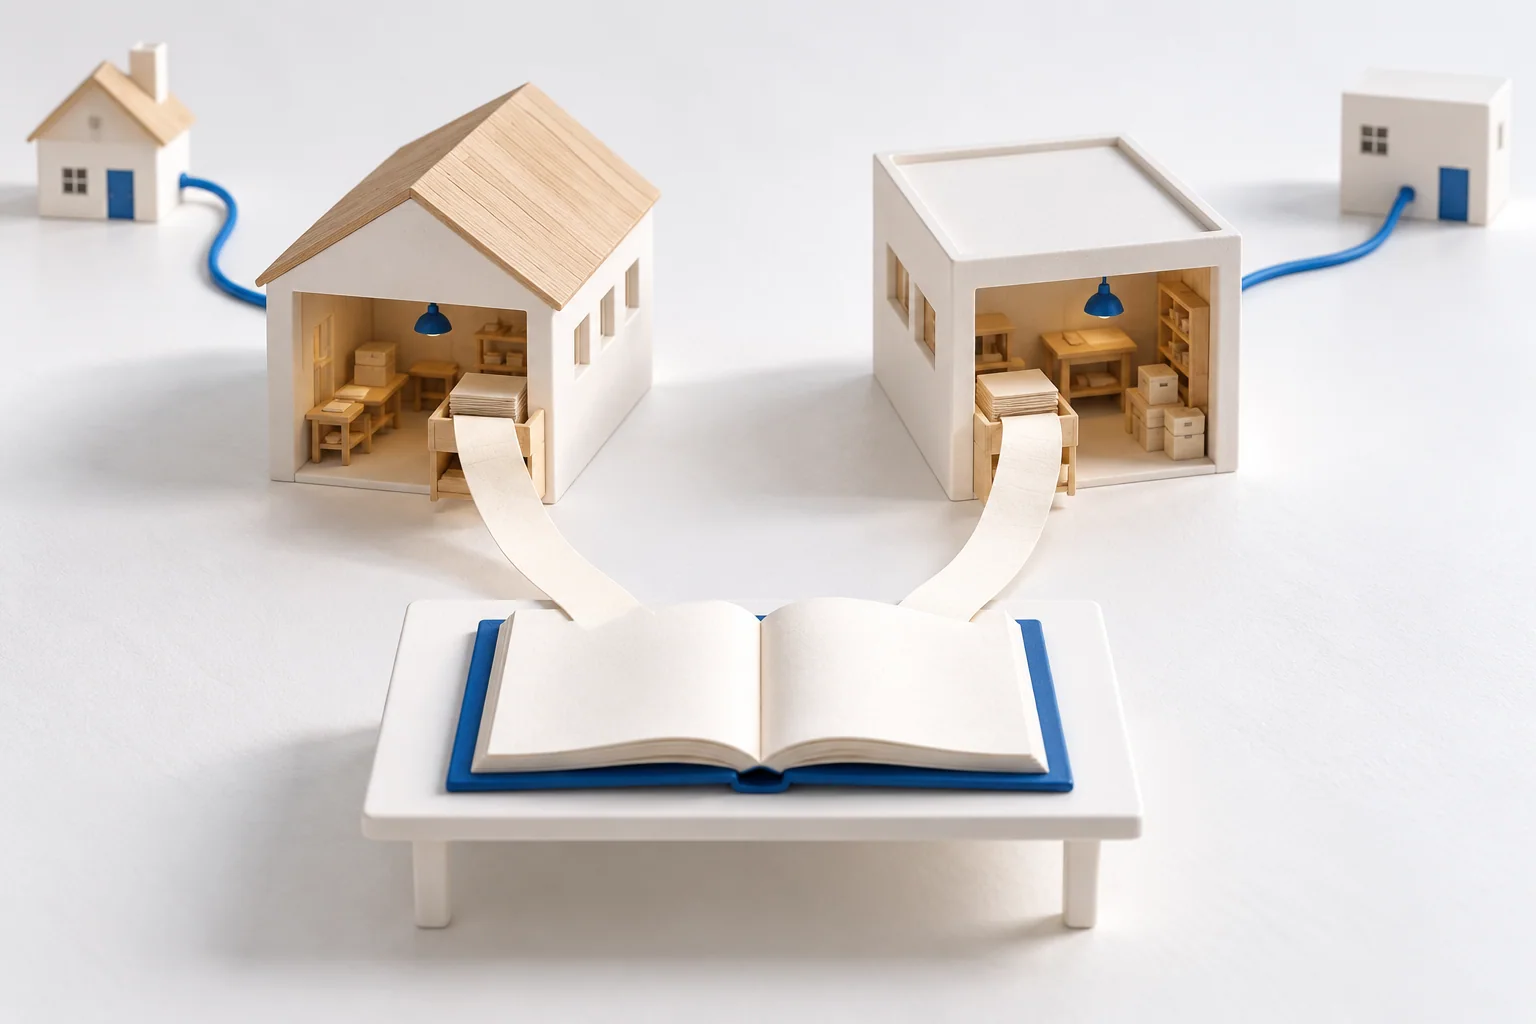
No single organization runs the whole Internet. Yet a network can depend on a small number of organizations for records, names and services that are difficult to replace. Both facts can be true at once.
To understand who has power, follow one ordinary task: opening a website. Someone operates the server, someone supplies connectivity, a naming system helps find the destination, and other networks decide how to carry the traffic. The dependencies between those roles matter more than an organization chart with one institution at the top.
Start with what each layer does
- Networks carry the traffic. Operators deploy equipment, connect to other networks and choose which routes to use. Those operational decisions determine where packets can travel.
- Names help people find destinations. The Domain Name System, or DNS, lets an application look up information associated with a name such as heng.lu. Domain registration and DNS hosting introduce their own providers and dependencies.
- Number registries maintain allocation records. Globally unique IP addresses and autonomous system numbers help independent networks work together. An autonomous system is a network, or group of networks, with a common routing policy.
- Institutions and law shape the terms. Policies, agreements and public law affect what the organizations involved can do. Their authority and responsibilities need to be examined separately from their technical capabilities.
IANA’s number-resource description explains the allocation hierarchy. RFC 7020 makes an important distinction: maintaining unique, accurate registration records is a registry responsibility; whether and how an address is announced in routing is an operational matter outside that registry system’s scope.
That is why a registry should not be pictured as a central router through which every connection passes. But a service can depend on its records even when its packets never pass through its offices.
How a small administrative role becomes a large source of power
Imagine an operator whose addresses appear in customer configurations, security rules and external systems. Changing them could mean coordinating with many other organizations. If the operator cannot replace its registry while retaining those identifiers, its dependence lasts as long as that switching problem remains.
In Note 42, Lu Heng examines how registration acquired economic power. Once networks and markets depend on an administrative record, discretion over the record can affect much more than the database. The operator carries the cost while the administrator may have far less at stake.
This is the heart of his critique: practical leverage has grown without a corresponding ability to replace the institution exercising it. “Nobody controls everything” is an incomplete answer when one dependency is enough to constrain a working network.
Why another provider is not always another way out
Moving a workload to a new hosting company can improve resilience. Buying an operational service can give an operator useful expertise and support. Neither change, by itself, proves that the underlying number-registration dependency has gone away.
If two providers rely on the same administrative record and the same unresolved restriction, switching between them may leave that point of failure intact. A contract can allocate responsibilities between its parties; it does not automatically replace every institution on which they rely.
The test is to follow the dependency one step further. What must keep working for the replacement service to work? Who controls that part? Can it also be replaced?
Keep the shared function; make the administrator replaceable
Lu Heng’s Bill of Rights of Uniqueness Coordination, Note 72, proposes a common layer limited to what networks need to work together. It pairs accurate records and unique identifiers with portability, auditability and replacement paths.
In practical terms, a transition has to preserve the evidence that lets others trust the records: who controls a resource, how it changed hands, and which security assertions remain valid. The point is to keep networks running through an institutional change, rather than require customers to depend on one institution indefinitely.
This is a design direction for a different coordination system. It calls for working alternatives that operators can adopt and verify. A promise to consult more widely leaves the central dependency in place; an exit that preserves continuity changes the relationship.
Begin with one service you rely on
Choose a website, cloud service or network connection and ask four questions:
- Which names, addresses and external records does it depend on?
- Who can change each of those records?
- What would users experience if that organization became unavailable or refused a necessary update?
- Can another provider take over without forcing users to change their network identity?
The answers reveal where independence is real and where it is only assumed. They also show why preparation is urgent: records, replacement arrangements and recovery procedures take time to establish. A dispute or outage is a poor moment to discover that the supposed alternative relies on the same gatekeeper.
Continue with a practical way to map governance risk. For the argument behind this approach, read Note 42: How a Neutral Bookkeeper Became a Fragile Power, then Note 72 on the rights a replacement system should preserve.